Altered | HackTheBox
A hard-difficulty Linux box centered on a Laravel password-reset flow brute-forced past rate limiting with spoofed IP headers, then a type-juggling bypass that unlocks SQL …
Read More →In-depth research and notes on security technologies, tradecraft, and lab write-ups.
A hard-difficulty Linux box centered on a Laravel password-reset flow brute-forced past rate limiting with spoofed IP headers, then a type-juggling bypass that unlocks SQL …
Read More →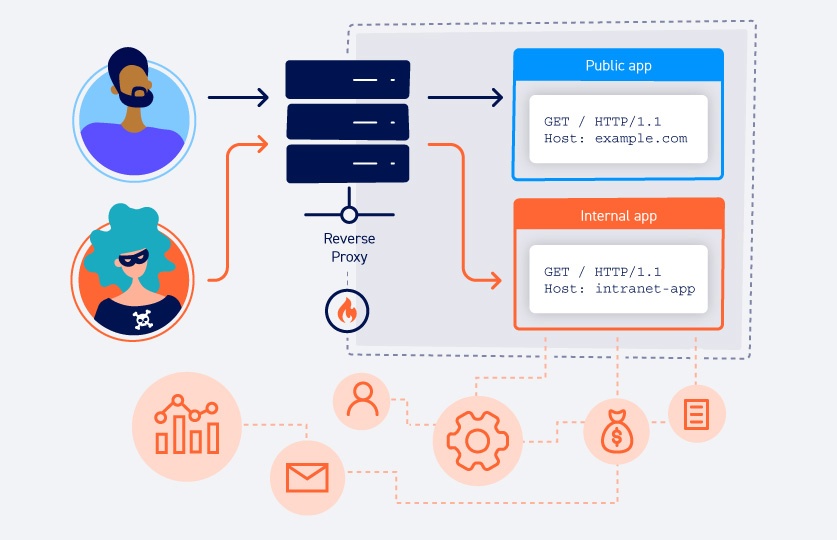
This post talks about how the Host header becomes an SSRF primitive, how front-end routing works, why trusting the Host header breaks the trust boundary between proxy and back-end, …
Read More →
A full breakdown of XML External Entity (XXE) injection: what it is, the XML internals that make it possible, where the attack surface hides, and a few examples of attack paths. …
Read More →
An easy-difficulty Linux box centered on a blind SQL injection in a registration form's country parameter, chained through sqlmap's FILE privilege abuse into a PHP webshell and …
Read More →
A web challenge centered on an AI 'Auto-mod copilot' that runs raw GraphQL queries on behalf of chat users with a privileged service account, allowing anyone to promote themselves …
Read More →
A web challenge involving Reflected DOM XSS in a museum catalog application, escalated to authenticated credential harvesting via same-origin fetch.
Read More →