Write-ups
In-depth research and notes on security technologies, tradecraft, and lab write-ups.
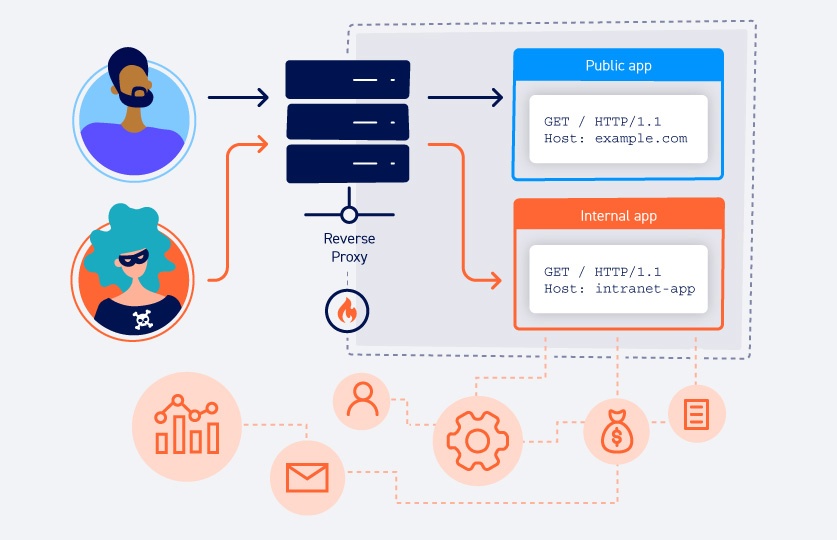
Routing-based SSRF via Host Header
This post talks about how the Host header becomes an SSRF primitive, how front-end routing works, why trusting the Host header breaks the trust boundary between proxy and back-end, …
Read More →
WIP - XXE Explained - WIP
A full breakdown of XML External Entity (XXE) injection: what it is, the XML internals that make it possible, where the attack surface hides, and a few examples of attack paths. …
Read More →